
Описание
User Role Editor WordPress plugin allows you to change user roles and capabilities easy.
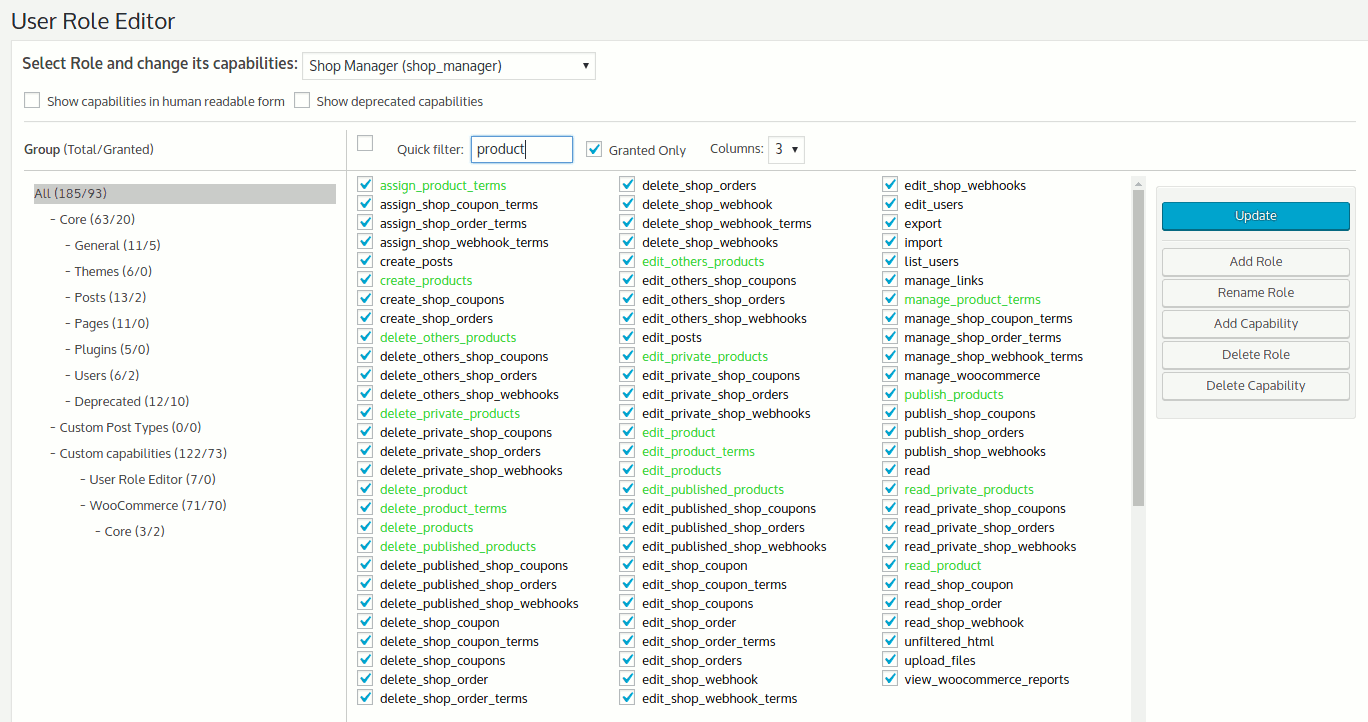
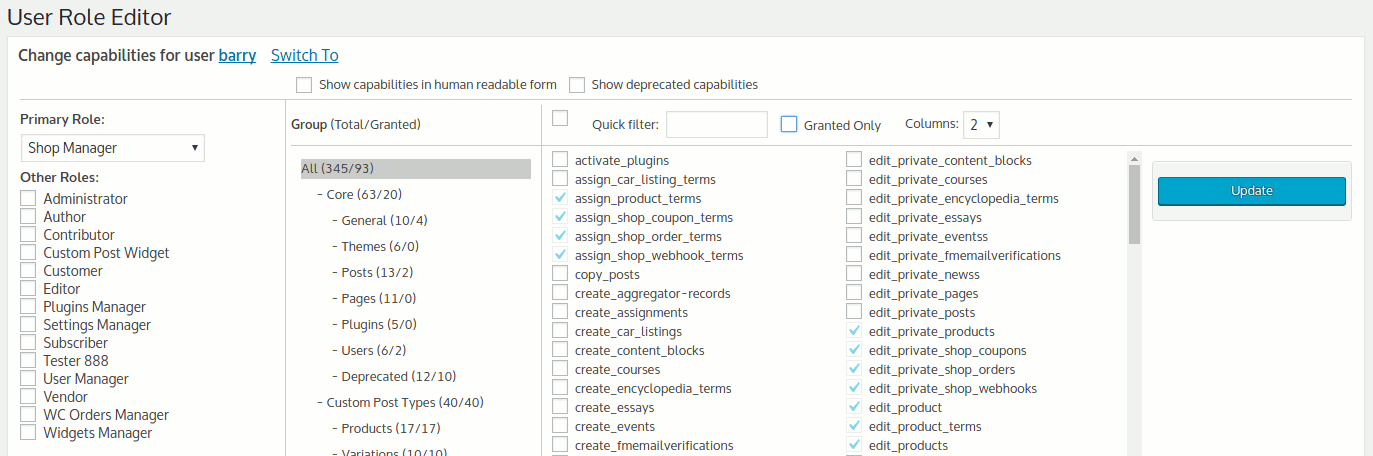
Just turn on check boxes of capabilities you wish to add to the selected role and click «Update» button to save your changes. That’s done.
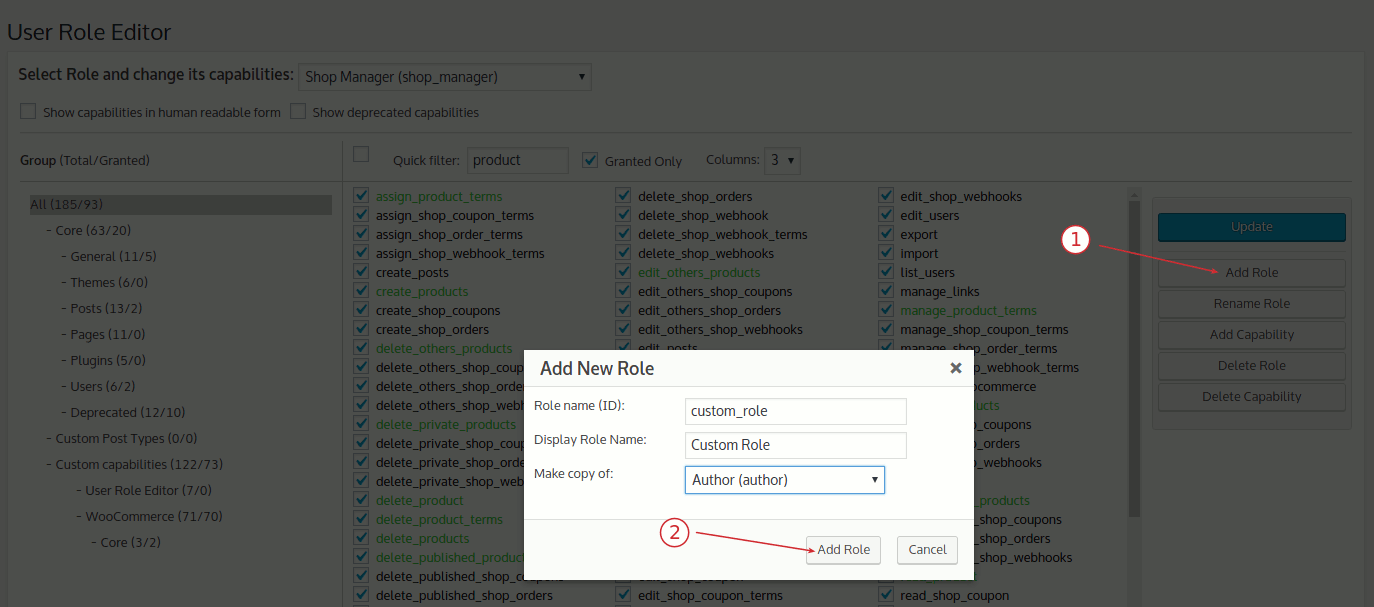
Add new roles and customize its capabilities according to your needs, from scratch of as a copy of other existing role.
Unnecessary self-made role can be deleted if there are no users whom such role is assigned.
Role assigned every new created user by default may be changed too.
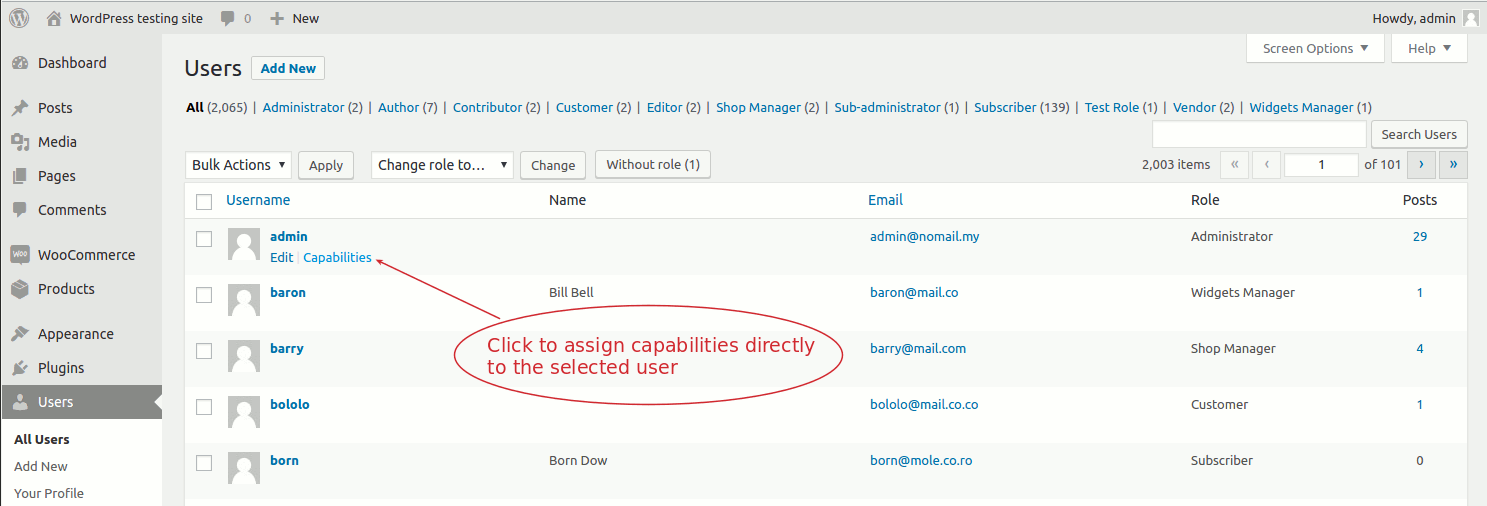
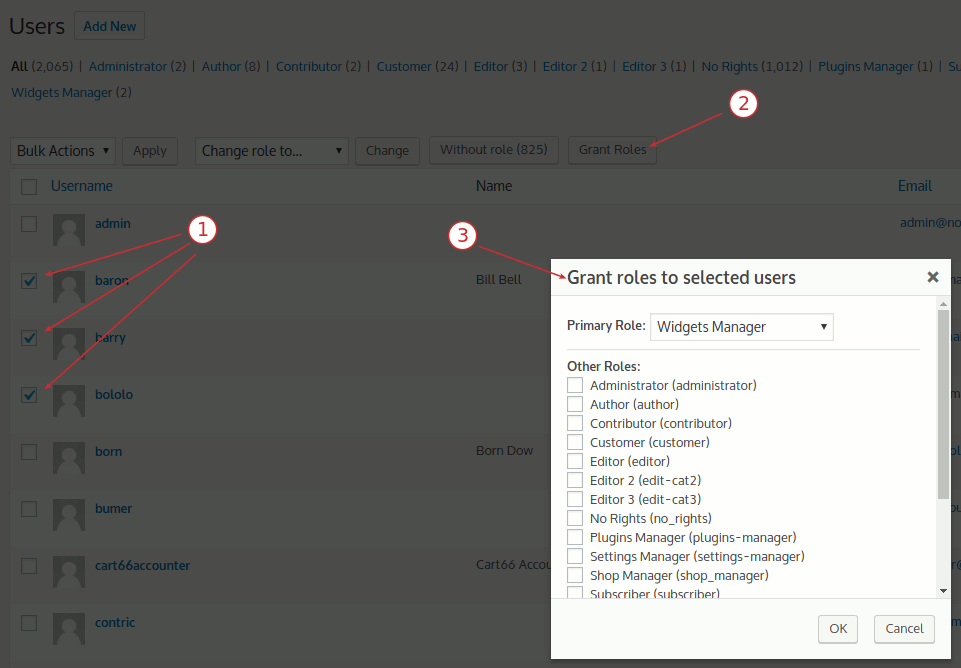
Capabilities could be assigned on per user basis. Multiple roles could be assigned to user simultaneously.
You can add new capabilities and remove unnecessary capabilities which could be left from uninstalled plugins.
Multi-site support is provided.
To read more about ‘User Role Editor’ visit this page
Вам нужна большая функциональность и качественная поддержка в режиме реального времени? Вы хотите убрать рекламу со страниц редактора ролей пользователей?
Купите Про-версию.
User Role Editor Pro включает в себя дополнительные модули:
- Заблокировать выбранные пункты меню администратора для данной роли.
- Hide selected front-end menu items for no logged-in visitors, logged-in users, roles.
- Заблокируйте определённые виджеты в меню «Внешний вид» для роли.
- Показывайте виджеты во фронт-энде для выбранных ролей.
- Block selected meta boxes (dashboard, posts, pages, custom post types) for role.
- «Export/Import» module. You can export user role to the local file and import it to any WordPress site or other sites of the multi-site WordPress network.
- Roles and Users permissions management via Network Admin for multisite configuration. One click Synchronization to the whole network.
- «Other roles access» module allows to define which other roles user with current role may see at WordPress: dropdown menus, e.g assign role to user editing user profile, etc.
- Управляйте доступом пользователей к редактированию записей/страниц/типов записей с помощью списка ID записей/страниц, авторов, таксономий.
- Управление доступом пользователей для выполнения операций активации и деактивации плагинов.
- Управление доступом пользователей к формам плагина Gravity Forms.
- Шорткод для отображения вложенного содержимого только пользователям с выбранными ролями.
- Ограничения на просмотр записей и страниц для выбранных ролей.
- Просмотр прав доступа к страницам админ-панели
Про-версия не содержит рекламы и включает премиум-поддержку.
Дополнительная документация
Ты можешь найти больше информации о плагине «Редактор Ролей Пользователей» на этой странице
I am ready to answer on your questions about plugin usage. Use plugin page comments for that.
Скриншоты
Установка
Порядок установки:
- Отключите плагин, если у вас установлена предыдущая версия.
- Extract «user-role-editor.zip» archive content to the «/wp-content/plugins/user-role-editor» directory.
- Активируйте плагин «User Role Editor» через меню ‘Плагины’ в панели администратора WordPress.
- Go to the «Users»-«User Role Editor» menu item and change your WordPress standard roles capabilities according to your needs.
Часто задаваемые вопросы
- Работает ли он с WordPress в многосайтовом окружении?
Да, он работает с многосайтовым WordPress. По умолчанию плагин работает для каждого блога из вашей многосайтовой сети так же, как и для локально установленного блога.
Чтобы обновить выбранную роль глобально для всей сети, вам следует установить флажок «Применить ко всем сайтам». Для использования редактора ролей пользователей в многосайтовой сети WordPress у вас должны быть привилегии суперадмина.
Про-версия позволяет управлять ролями всей сети из Netwok Admin.
To read full FAQ section visit this page at shinephp.com.
Отзывы


Участники и разработчики
«User Role Editor» — проект с открытым исходным кодом. В развитие плагина внесли свой вклад следующие участники:
Участники
«User Role Editor» переведён на 28 языков. Благодарим переводчиков за их работу.
Перевести «User Role Editor» на ваш язык.
Заинтересованы в разработке?
Посмотрите код, проверьте SVN репозиторий, или подпишитесь на журнал разработки по RSS.
Журнал изменений
[4.66.1] 25.08.2026
- Fix: URE_Assign_Role::$lib property was changed to protected.
- Fix: URE_Uninstall::delete_options() private function changed to protected.
- Fix: URE_Uninstall::init_options_list() referenced ‘ure_task_queue’, which never matched URE_Task_Queue::OPTION_NAME (‘ure_tasks_queue’), so that option was never deleted on uninstall.
- Fix: URE_Core::define_files() — class URE_Uninstall was not added correctly, null was written instead of class name.
- Fix: activating Pro while free was already active caused a fatal «Cannot redeclare ure_log_error()» error; the function declaration is now guarded with function_exists().
- Fix: activating this plugin while the paired Pro plugin was already active silently left both active instead of deactivating the paired one, because the register_activation_hook() call never ran in that request; it’s now registered as a standalone function directly in the main plugin file, ahead of the class_exists(‘URE_Loader’) guard that was skipping it.
[4.66] 19.08.2026
- Обновление: Отмечено как совместимое с WordPress 7.1
- Требуемая версия PHP повышена до 7.4
- Требуемая версия WordPress повышена до 4.6
- Обновление: Усовершенствован код загрузки плагина.
- Update: Plugin does not use self-defined PHP global constants. Needed data moved inside classes.
- Update: URE_Admin_Notice class output was escaped with esc_attr(), wp_kses_post() functions.
- Security Fix: SQL queries in URE_Editor::direct_network_roles_update() and leave_roles_for_blog() are passed to $wpdb->prepare() with real %s placeholders.
- Security Fix: URE_Editor::get_caps_columns_quant() now requires a valid nonce before writing a display-preference transient from $_POST, closing a minor CSRF gap.
- Fix: URE_Protect_Admin used a bitwise «&» instead of a logical «&&» when checking a capabilities array, which could throw a PHP 8 TypeError; fixed to use «&&», and the related IN() SQL clause is now hardened with array_map(‘absint’, …).
- Update: nonce actions used on the Settings/Tools pages are now scoped per form (ure_settings_update, ure_addons_settings_update, ure_default_roles_update, ure_settings_ms_update, ure_settings_tools_exec) instead of one shared string.
- Update: additional output escaping was added across URE_View, URE_Role_View and URE_Role_Additional_Options (role/capability slugs, wp_json_encode() instead of json_encode(), esc_url() on form actions), plus a defense-in-depth capability check in URE_Role_Additional_Options::save().
- Update: rel=»noopener noreferrer» was added to external links opened with target=»_new».
- Update: hardcoded text strings in the role editor toolbar are now translatable.
- Fix: URE_Assign_Role used the %i SQL placeholder, which needs WordPress 6.2+, below the plugin’s declared minimum; replaced with direct interpolation of internal table names.
- Fix: URE_Editor::reset_user_roles() had an unescaped wp_die() message; further output escaping (esc_url(), esc_html(), absint()) was added across URE_Base_Lib, URE_Editor, URE_User_Other_Roles and URE_User_View.
- Fix: several request-var/database-result comparisons that could be bypassed by PHP type juggling are now strict, including URE_Grant_Roles::is_try_remove_admin_from_himself()’s «can’t remove your own admin role» check.
- Fix: URE_Base_Lib::set() now correctly rejects unknown properties instead of silently creating them; URE_View declares its $advert property explicitly.
- Update: $_SERVER[‘REQUEST_URI’] is now validated and unslashed before sanitizing in URE_Lib::is_right_admin_path() and URE_User_Other_Roles::is_user_profile_extention_allowed().
- Update: posted role IDs are now sanitized (sanitize_key(), wp_unslash()) in URE_Editor, and its ‘object’/role-selection request parameters are constrained to known values.
- Update: URE_Base_Lib::get_blog_ids() now uses get_sites() instead of a raw database query.
- Update: URE_Capability::revoke_caps() now uses get_users() instead of a raw database query.
- Update: URE_Protect_Admin::has_administrator_role() now uses user_can() instead of a raw database query.
[4.65] 21.05.2026
- Обновление: Отмечен как совместимый с WordPress 7.0
- Обновление: Разметка страниц была изменена в соответствии с изменениями CSS в WordPress 7.0.
- Update: «defined(‘ABSPATH’)» guard was added to all PHP files to exclude PHP files direct execution.
- Update: sanitize_text_field(), sanitize_key(), sanitize_url() functions are used to secure user input before processing.
- Update: _nonce field checking was added before data update in addition to test made already on the higher level.
Файл changelog.txt содержит полный список изменений.